ARP Certificate Home

Category

Network Security

26 articles

Cloud-Native Environments Have Rendered Traditional ARP Spoofing Defenses Largely Ineffective — Here Is What Security Teams Must Do Instead

Cloud-Native Environments Have Rendered Traditional ARP Spoofing Defenses Largely Ineffective — Here Is What Security Teams Must Do Instead

The mitigation strategies that reliably contained ARP spoofing in on-premises environments were designed for a world of fixed broadcast domains, managed switches, and predictable trust boundaries — none of which exist in modern cloud-native infrastructure. This article examines why legacy defenses fail in hybrid and multi-cloud contexts, and outlines the specific architectural and procedural controls that actually provide protection today.

How One SOC Team's ARP Audit Stopped a Lateral Movement Attack That Had Been Hiding for Weeks

How One SOC Team's ARP Audit Stopped a Lateral Movement Attack That Had Been Hiding for Weeks

A mid-market financial services firm discovered a sophisticated lateral movement campaign only after a targeted ARP audit surfaced behavioral anomalies that conventional monitoring had dismissed as noise. This forensic case study walks through the specific indicators, procedural gaps, and detection rules that made the difference between containment and catastrophe.

Anatomy of a Supply Chain Breach: How Gratuitous ARP Manipulation Enabled Persistent Network Access Across a Manufacturing Environment

Anatomy of a Supply Chain Breach: How Gratuitous ARP Manipulation Enabled Persistent Network Access Across a Manufacturing Environment

A fictionalized but technically accurate forensic case study reconstructs how an attacker exploited gratuitous ARP behavior to achieve persistent lateral movement within a manufacturing supply chain network. The analysis details each phase of the attack, the detection failures that allowed it to persist, and the specific defensive controls that could have interrupted the intrusion chain.

Kubernetes and the ARP Security Gap: Why Container Networking Has Outpaced the Tools Designed to Protect It

Kubernetes and the ARP Security Gap: Why Container Networking Has Outpaced the Tools Designed to Protect It

Containerized infrastructure has fundamentally altered the Layer 2 attack surface in ways that traditional ARP security tooling was never designed to address. Kubernetes networking models introduce ARP behaviors that legacy intrusion detection systems cannot interpret accurately, leaving security teams with visibility gaps they may not know exist. This article examines the specific ARP vulnerabilities that emerge in container orchestration environments and the detection strategies capable of add

Alert Fatigue Is Winning: How Misconfigured ARP Detection Rules Are Blinding Your Security Team to Real Threats

Alert Fatigue Is Winning: How Misconfigured ARP Detection Rules Are Blinding Your Security Team to Real Threats

ARP monitoring systems generate some of the highest alert volumes in enterprise security operations—yet most of that volume is noise. When detection rules are poorly tuned, analysts stop trusting the data, and genuine attacks pass through uncontested. This article examines the structural misconfigurations driving ARP alert fatigue and offers a practical framework for restoring signal integrity in production environments.

Vendor-Shipped ARP Flaws: A Procurement Audit Framework for Security Teams Who Cannot Afford to Assume Compliance

Vendor-Shipped ARP Flaws: A Procurement Audit Framework for Security Teams Who Cannot Afford to Assume Compliance

Enterprise network equipment has shipped from major vendors with documented ARP implementation flaws that persisted undetected through deployment and into production. Security teams that rely on vendor reputation rather than protocol-level verification are accepting risk they may not be able to quantify. This article outlines a structured audit approach for evaluating third-party equipment before it reaches your infrastructure.

Your First ARP Lab Will Break — Here Is Exactly Why and How to Rebuild It Correctly

Your First ARP Lab Will Break — Here Is Exactly Why and How to Rebuild It Correctly

Most IT professionals underestimate how many configuration pitfalls await them in their first ARP lab environment. From misconfigured packet captures to incorrect VLAN assignments, the early failures are predictable — and entirely fixable. This guide walks certification candidates through the most common setup errors and the precise steps needed to correct them before exam day.

Reading the Past From ARP Logs: A Forensic Analyst's Guide to Reconstructing Network Events After the Fact

Reading the Past From ARP Logs: A Forensic Analyst's Guide to Reconstructing Network Events After the Fact

When conventional network telemetry is absent, corrupted, or deliberately erased, ARP logs and cache artifacts frequently contain the residual evidence that makes incident reconstruction possible. For forensic analysts and incident responders who know how to read them, these records can establish attack timelines, identify spoofing activity, and produce evidence chains that withstand scrutiny in post-incident reviews. This guide provides a structured framework for extracting that intelligence wh

How Hybrid Infrastructure Breaks Layer 2 Security — And What ARP Exposes When It Does

How Hybrid Infrastructure Breaks Layer 2 Security — And What ARP Exposes When It Does

Hybrid deployments — spanning on-premises switching infrastructure, cloud virtual networks, and edge computing nodes — introduce ARP attack surfaces that conventional segmentation strategies were never designed to address. As enterprise architectures grow more distributed, the assumptions embedded in traditional Layer 2 security controls become liabilities rather than protections. This technical examination walks through the architectural patterns, threat scenarios, and validation techniques tha

The Layer 2 Blind Spot That Most Penetration Tests Never Reach — And What Attackers Do With It

The Layer 2 Blind Spot That Most Penetration Tests Never Reach — And What Attackers Do With It

Most penetration testing engagements stop well short of the protocol layer where ARP vulnerabilities live, leaving organizations with a false sense of validated security. Attackers who understand Layer 2 mechanics exploit precisely the gaps that standard pen test methodologies overlook. Security teams that fail to demand protocol-level testing are, in effect, auditing only half of their attack surface.

The Compliance Blind Spot Hiding in Plain Sight: Why Auditors Must Start Taking ARP Seriously

The Compliance Blind Spot Hiding in Plain Sight: Why Auditors Must Start Taking ARP Seriously

SOC 2, ISO 27001, and HIPAA have long concentrated their scrutiny on Layer 3 and above, leaving Address Resolution Protocol largely untouched by formal audit processes. This oversight creates measurable vulnerabilities in enterprise compliance posture that adversaries are well-positioned to exploit. Understanding why ARP falls through the regulatory cracks—and how to close that gap—is now a professional imperative for IT security teams.

When Segmentation Fails Silently: How ARP Behavior Exposes the Gaps in Your Subnet Isolation Strategy

When Segmentation Fails Silently: How ARP Behavior Exposes the Gaps in Your Subnet Isolation Strategy

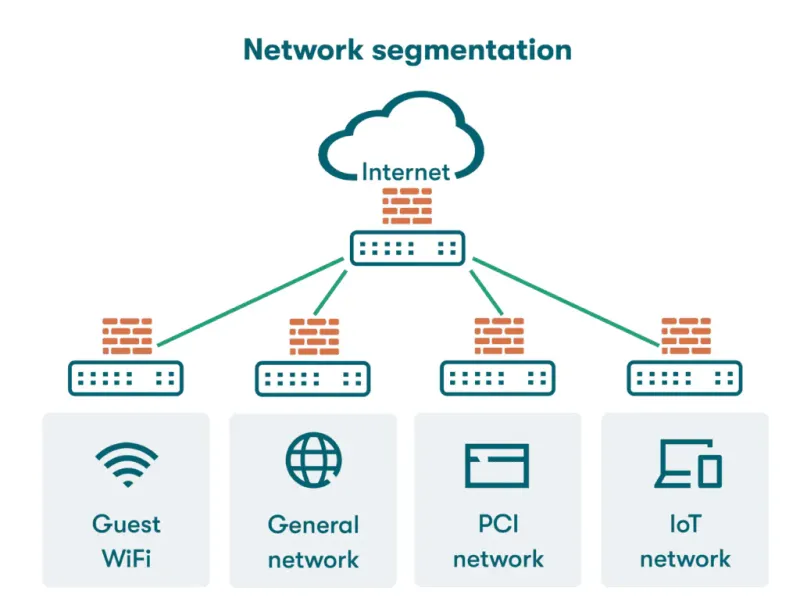
Organizations frequently invest significant resources in network segmentation, only to find that ARP traffic quietly crosses boundaries they assumed were secure. This article examines how misconfigured ARP behavior at Layer 2 undermines subnet isolation, why compliance frameworks rarely catch these gaps, and what IT security professionals must do to diagnose and remediate them before attackers exploit the exposure.

The ARP Proxy Problem: How Flawed Assumptions Are Quietly Undermining Enterprise Network Architecture

The ARP Proxy Problem: How Flawed Assumptions Are Quietly Undermining Enterprise Network Architecture

ARP proxy is one of the most misunderstood mechanisms in enterprise networking, and the consequences of that misunderstanding extend far beyond misconfiguration. Security teams operating in hybrid and multi-subnet environments routinely make architectural decisions based on assumptions about ARP proxy behavior that simply do not hold under real-world conditions. This article examines the gap between perceived and actual ARP proxy behavior—and what correcting that gap means for your network's sec

Zero-Trust Has a Layer 2 Blind Spot — And ARP Is Standing Right in It

Zero-Trust Has a Layer 2 Blind Spot — And ARP Is Standing Right in It

Zero-trust architecture has reshaped how enterprises think about access control and identity verification, yet most implementations stop short of addressing ARP at the protocol level. This gap leaves Layer 2 environments exposed even when Layer 3 and above appear tightly governed. Understanding where ARP fits within microsegmentation policy is no longer optional for organizations pursuing NIST or CIS compliance.

Why Your On-Premises ARP Playbook Breaks Down the Moment You Move to the Cloud

Why Your On-Premises ARP Playbook Breaks Down the Moment You Move to the Cloud

Security teams that built rigorous ARP defenses for physical networks are discovering those controls offer little protection once workloads migrate to AWS, Azure, or GCP. The fundamental way each cloud provider handles address resolution diverges sharply from traditional Ethernet behavior, creating blind spots that hybrid environment managers rarely anticipate. This article examines those divergences in detail and outlines provider-specific mitigation strategies that align with modern certificat

Dynamic ARP Inspection Deployments That Keep Failing: A Compliance-Ready Troubleshooting Framework for Security Teams

Dynamic ARP Inspection Deployments That Keep Failing: A Compliance-Ready Troubleshooting Framework for Security Teams

Despite widespread awareness of Dynamic ARP Inspection as a critical security control, many organizations discover during audits that their DAI configurations are incomplete, misconfigured, or entirely ineffective in production. This article examines the root causes behind failed ARP inspection rollouts and provides a structured framework security teams can use to validate, correct, and future-proof their implementations before the next compliance review.

Gratuitous ARP: The Overlooked Broadcast Behavior That Exposes More About Your Network Than You Realize

Gratuitous ARP: The Overlooked Broadcast Behavior That Exposes More About Your Network Than You Realize

Gratuitous ARP packets are transmitted across enterprise networks thousands of times daily, yet most security teams treat them as routine background noise. Understanding what these unsolicited broadcasts actually communicate—about device behavior, network architecture, and potential adversarial activity—can transform how organizations approach threat intelligence at the protocol level.

How Default ARP Timeout Settings Are Quietly Sabotaging Your Compliance Posture

How Default ARP Timeout Settings Are Quietly Sabotaging Your Compliance Posture

Across SOC 2, PCI-DSS, and HIPAA audits, misconfigured ARP timeout values are emerging as an overlooked source of compliance violations that catch even seasoned security teams off guard. Understanding the relationship between ARP cache duration and regulatory requirements is no longer optional for IT professionals responsible for audit readiness. This article examines where default configurations fall short and how practitioners can close those gaps before auditors do.

When ARP Caches Expire Too Soon: The Hidden Configuration Flaw Draining Enterprise Network Reliability

When ARP Caches Expire Too Soon: The Hidden Configuration Flaw Draining Enterprise Network Reliability

Misconfigured ARP cache timeouts and TTL values are quietly triggering authentication failures, performance degradation, and compliance blind spots across enterprise infrastructure. This technical investigation examines how a single overlooked parameter can cascade into widespread network instability—and what IT teams can do to diagnose and correct it before auditors or adversaries exploit the gap.

Low-and-Slow ARP Flooding: The Bandwidth Attack Your Monitoring Dashboard Will Never Flag

Low-and-Slow ARP Flooding: The Bandwidth Attack Your Monitoring Dashboard Will Never Flag

Sophisticated attackers are exploiting a fundamental blind spot in conventional network monitoring by sustaining low-volume ARP floods over weeks rather than launching obvious burst attacks. Traditional threshold-based alerting systems are structurally ill-equipped to detect these gradual degradation campaigns. This article examines the mechanics of the technique, documents real-world organizational impact, and outlines actionable detection strategies that security teams can deploy today.

Protocol-Level ARP Validation: Building the First Line of Defense Before Threats Reach Your Network Perimeter

Protocol-Level ARP Validation: Building the First Line of Defense Before Threats Reach Your Network Perimeter

Most enterprise security architectures address threats after they've already entered the network — but ARP validation frameworks shift that posture by verifying device identity at the protocol level before access is ever granted. This deep dive examines the technical mechanisms, emerging toolsets, and architectural principles that define modern ARP validation. Security professionals who command this knowledge are increasingly positioned as indispensable architects within their organizations.

Enterprise Networks Are Still Losing the Battle Against ARP Spoofing — Here's What Security Teams Must Do Now

Enterprise Networks Are Still Losing the Battle Against ARP Spoofing — Here's What Security Teams Must Do Now

ARP spoofing remains one of the most persistent and underestimated threats facing enterprise networks in 2024, exploiting a foundational protocol that was never designed with security in mind. Despite decades of documented vulnerabilities, organizations across every industry continue to fall victim to man-in-the-middle attacks, credential harvesting, and session hijacking rooted in ARP manipulation. This deep-dive examines the modern attack landscape and delivers concrete, implementable defenses